Network Segmentation Services in Flemington, NJ

Build a More Secure, Controlled, and Efficient Network

Create Clearer Network Boundaries. Strengthen Your Network.

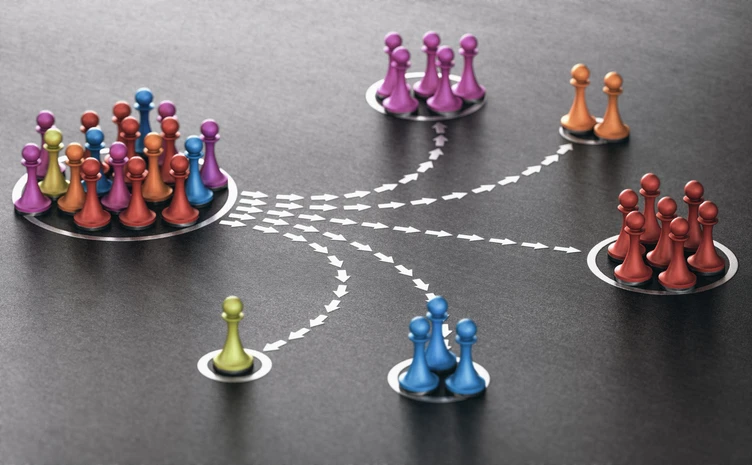
Network segmentation services help organizations divide an IT network into smaller, controlled sections based on business function, security requirements, applications, users or data sensitivity. Instead of allowing devices and workloads to communicate broadly across a single network, segmentation establishes defined boundaries that determine where traffic can travel and who or what can access specific resources.

A network segmentation strategy can include network assessment, asset discovery, data-flow mapping, network design, firewall configuration, virtual local area networks (VLANs), access control lists (ACLs), monitoring, and ongoing policy management. The appropriate approach depends on how an organization operates, where its applications are hosted, and what information must be protected.

Network segmentation can support a broader network security strategy by limiting unnecessary communication between systems. It can also help organizations isolate sensitive environments, reduce congestion, and maintain clearer control over access to important resources such as customer databases.

TeamLogic IT in Flemington works with businesses as an managed IT services provider and technology partner. Network segmentation services may include evaluating the existing environment, helping develop segmentation policies, assisting with implementation, and providing ongoing monitoring and management based on an organization’s technology requirements.

Strengthen Your Security with Network Segmentation.

Protect your business from cyber threats by separating critical systems, sensitive data and network traffic. TeamLogic IT's Network Segmentation Services help reduce security risks, limit unauthorized access and prevent threats from spreading across your network. Take control of your IT infrastructure with a smarter, more secure network strategy.

Types of Network Segmentation

Network segmentation can be implemented in several ways. Many organizations use multiple segmentation methods together rather than relying on a single technology.

Macro-segmentation separates large portions of a network according to broad categories. For example, an organization might create separate network zones for employees, servers, guest devices, operational technology, and customer-facing systems. Macro-segmentation creates clearly defined boundaries between major technology environments.

Micro segmentation takes a more granular approach. Rather than separating large network areas, micro segmentation can create secure zones around specific workloads, applications, or services. Policies may determine which workloads can communicate and under what circumstances. This level of control is commonly associated with Zero Trust principles because access is based on specific requirements rather than general network location.

Network Segmentation

How Network Segmentation Works

Network segmentation works by establishing defined communication boundaries and applying rules to traffic moving between those boundaries. One important distinction is between north-south traffic and east-west traffic.

North-south traffic typically moves between an internal network and external resources, such as internet traffic passing through a perimeter firewall. East-west traffic moves between systems inside an organization’s environment, such as communication between application servers, databases and employee devices.

Traditional security strategies often concentrate heavily on north-south traffic. Modern segmentation also addresses east-west traffic because internal systems do not necessarily need unrestricted access to one another. Enforcement points can include firewalls, routers, switches, ACLs, cloud security controls, and software-defined policies. These technologies examine traffic and determine whether communication is permitted based on established rules.

For example, employees in a sales department may need access to a customer relationship management platform but may not require direct access to the database servers supporting that application. A segmentation policy can permit the necessary application traffic while restricting unnecessary direct connections.

How Network Segmentation Works

Implementing Network Segmentation

Effective network segmentation usually begins with understanding the existing environment before creating new restrictions. The first step is to assess the network and map connected assets. This can include servers, workstations, mobile devices, printers, network equipment, applications, cloud workloads, and Internet of Things devices. IT teams should also document how those assets communicate.

Assets can then be classified according to their role and sensitivity. Customer databases, financial systems, administrative tools, and other sensitive resources may require tighter controls than general-purpose employee systems.

Organizations should define both security and performance goals before creating segmentation policies. A security goal may be limiting direct employee access to sensitive databases. A performance goal may involve separating high-volume traffic so that it does not contribute unnecessary congestion elsewhere on the network. Network security policies define which types of communication should be permitted. Role-based access policies can then associate those requirements with employees, systems or applications.

Firewall rules and ACLs translate those policies into technical enforcement controls. Before implementing them broadly, organizations can pilot segmentation within a controlled portion of the network. Pilot deployments help IT teams validate communication requirements, identify unexpected dependencies and confirm that important applications continue to operate as intended. Traffic should then be monitored after implementation, with policies adjusted as business requirements and technology environments change.


Implementing Network Segmentation

Data Center Segmentation Considerations

Data centers often contain systems with very different functions and sensitivity levels. Segmentation can separate web servers, application servers, databases, administrative systems, backup environments and other infrastructure.

VLANs are commonly used to create logical zones without requiring separate physical switches for each environment. Organizations with specialized requirements may also use physical separation where dedicated hardware provides an appropriate operational boundary.

Firewall rules can control east-west traffic between data center segments. For example, a front-end application may be allowed to communicate with a designated application server, while direct communication from user workstations to a database segment is restricted.

Data center segmentation is generally best approached in phases. Introducing large numbers of new restrictions at once can affect applications with undocumented dependencies. A phased deployment allows teams to test each segment, observe traffic and refine policies before expanding the design.

 Data Center Segmentation Considerations

Network Security and Compliance

Network segmentation should be considered part of a broader network security strategy rather than an isolated control. Firewalls, identity controls, endpoint security, monitoring, logging and access management all contribute to how effectively segmentation works. Policies should reflect actual business requirements and should be reviewed as systems, applications and personnel change.

For organizations subject to PCI DSS, segmentation can help separate payment-related systems from general corporate traffic. Doing so may help organizations define the scope of the cardholder data environment more clearly.

Logging is also important. Firewall logs, authentication records and traffic monitoring data can document how access policies are being enforced. Organizations may integrate this information with a security information and event management (SIEM) platform to support centralized monitoring and audit preparation.

Customer databases deserve particular attention. Access should be based on legitimate business and application requirements rather than broad network availability. Segmentation can help create additional boundaries around these systems while allowing authorized applications and users to perform necessary functions.

Compliance remains the organization’s responsibility. Technology controls such as segmentation can support IT compliance efforts, documentation and audit readiness, but legal counsel, assessors and other appropriate professionals should determine specific regulatory or contractual obligations.


Common Components of Network Edge Protection

Network Performance Considerations

Network segmentation should support security objectives without creating unnecessary performance problems. Every enforcement point introduces some level of processing. Firewalls may inspect traffic, routers may apply ACLs, and cloud security controls may evaluate communication between workloads. Poorly designed rules or undersized infrastructure can contribute to throughput limitations or latency.

Organizations should therefore establish a performance baseline before implementation. Monitoring normal bandwidth use, application response times, and traffic patterns provides a reference point for evaluating changes after segmentation is introduced.

Traffic monitoring should continue after deployment. If a new firewall boundary creates a bottleneck, the issue may involve firewall capacity, routing design, or an application generating more cross-segment traffic than expected.

Quality of Service (QoS) can also be paired with segmentation where appropriate. QoS policies can prioritize latency-sensitive services such as voice or video, while segmentation determines which systems are permitted to communicate.

Network Management That Scales With Your Business

Access Policies and Network Security Policies

Network segmentation depends on clearly defined access policies. A least-privilege policy grants users, applications and devices only the access required to perform their authorized functions. Rather than allowing a department or device category broad access to the network, administrators identify the specific services and systems that are needed. Role-based access policies organize permissions around business functions. For example, an employee may receive network access based on membership in a finance, human resources or IT administration role.

Application and service accounts can follow similar principles. Policies should not remain static indefinitely. Organizations should establish a review cadence based on their environment and business requirements. Reviews may also be appropriate when new applications are deployed, departments change responsibilities or infrastructure is migrated.

Documenting policies is equally important. Documentation can include the purpose of each segment, permitted communication paths, responsible system owners and the business justification for exceptions. These records can support troubleshooting, change management and audit readiness.

Network Security Policies

Firewall Rules and Enforcement

Firewall rules translate network security policies into specific technical controls. A common approach is to use a deny-by-default model for sensitive segments. Under this model, traffic is denied unless a rule explicitly permits a required connection.

For example, a database segment might deny inbound connections by default while allowing only a designated application server to connect on an approved database port. An administrative network might allow management connections from authorized IT systems while restricting access from standard user devices. Policies can also be translated into router or switch ACLs. An ACL may permit traffic from an approved subnet to a particular service while denying traffic from unrelated networks.

Rule sets should remain as clear as possible. Overlapping, duplicate or outdated rules can make firewall management more difficult and may produce unintended access paths. Organizations should document changes and periodically review rules to confirm that they continue to support current requirements.

Automated firewall management or auditing tools can assist with identifying unused, conflicting or overly broad rules. Human review remains important because technical configuration must still reflect business context.

Firewall Rules and Enforcement

Network Segmentation by TeamLogic IT

TeamLogic IT in Flemington helps organizations evaluate where network segmentation fits within their broader IT and network security strategy. An assessment engagement can begin with reviewing network architecture, identifying connected assets and documenting existing communication patterns. The resulting information can help determine which systems should be separated and which communication paths are necessary for business operations.

Segmentation planning may also include recommendations for VLANs, firewall boundaries, access controls and monitoring. Where appropriate, proposed policies can be tested through a pilot deployment before they are introduced more broadly.

During implementation, support may include configuring switches and firewalls, establishing VLANs, developing ACLs and validating connectivity. Both remote and onsite assistance may be available depending on the requirements of the organization and participating TeamLogic IT location.

After deployment, managed monitoring and policy maintenance can help organizations evaluate traffic patterns, address configuration changes and keep segmentation aligned with evolving infrastructure. Network changes should be reviewed as new applications, users, cloud services and devices are introduced.

TeamLogic IT in Flemington approaches network segmentation as part of an organization’s broader technology environment, connecting network design, access control, monitoring and ongoing IT management.

Why TeamLogic IT’s Data Protection Services Work

Next Steps and Contact

Network segmentation is most effective when it reflects how an organization’s users, applications, data and infrastructure actually interact. A successful project begins with understanding the current environment and identifying which systems require additional separation or access controls.

TeamLogic IT can help assess your network, evaluate segmentation opportunities and develop an implementation approach aligned with your technology requirements. Depending on the engagement and participating location, support may include network assessment, segmentation planning, pilot implementation, firewall and VLAN configuration, monitoring and ongoing policy management.

Next Steps

Request a Consultation

Reliable network monitoring starts with understanding what needs to be monitored, what information matters, and how IT teams will respond when conditions change. A network assessment can provide a useful starting point. TeamLogic IT can help evaluate existing network devices, infrastructure, traffic patterns, monitoring practices, and business requirements to identify areas where additional visibility may be useful.  From there, your organization can develop a monitoring roadmap that prioritizes appropriate tools, alerts, workflows, and remediation needs.